256 bit and 512 bit encryption are somewhat common. A 256 bit private key is 64 characters long (I’m simplifying this, don’t @ me about it being hex). A 512 bit private key is twice as long. That long string of random characters is what gives this type of encryption its power. It’s essentially unguessable, even with a computer and a lot of time.
Using “4” as your private key would significantly undermine security. Hackers can’t check every possible option for a 512 bit key, but they can certainly (and trivially) try simple numbers padded by 0’s, like our “4” private key.
You’ve taken a strong and proven system and made it trivially weak. That’s the joke. It’s not that funny, but that’s what you’re missing.


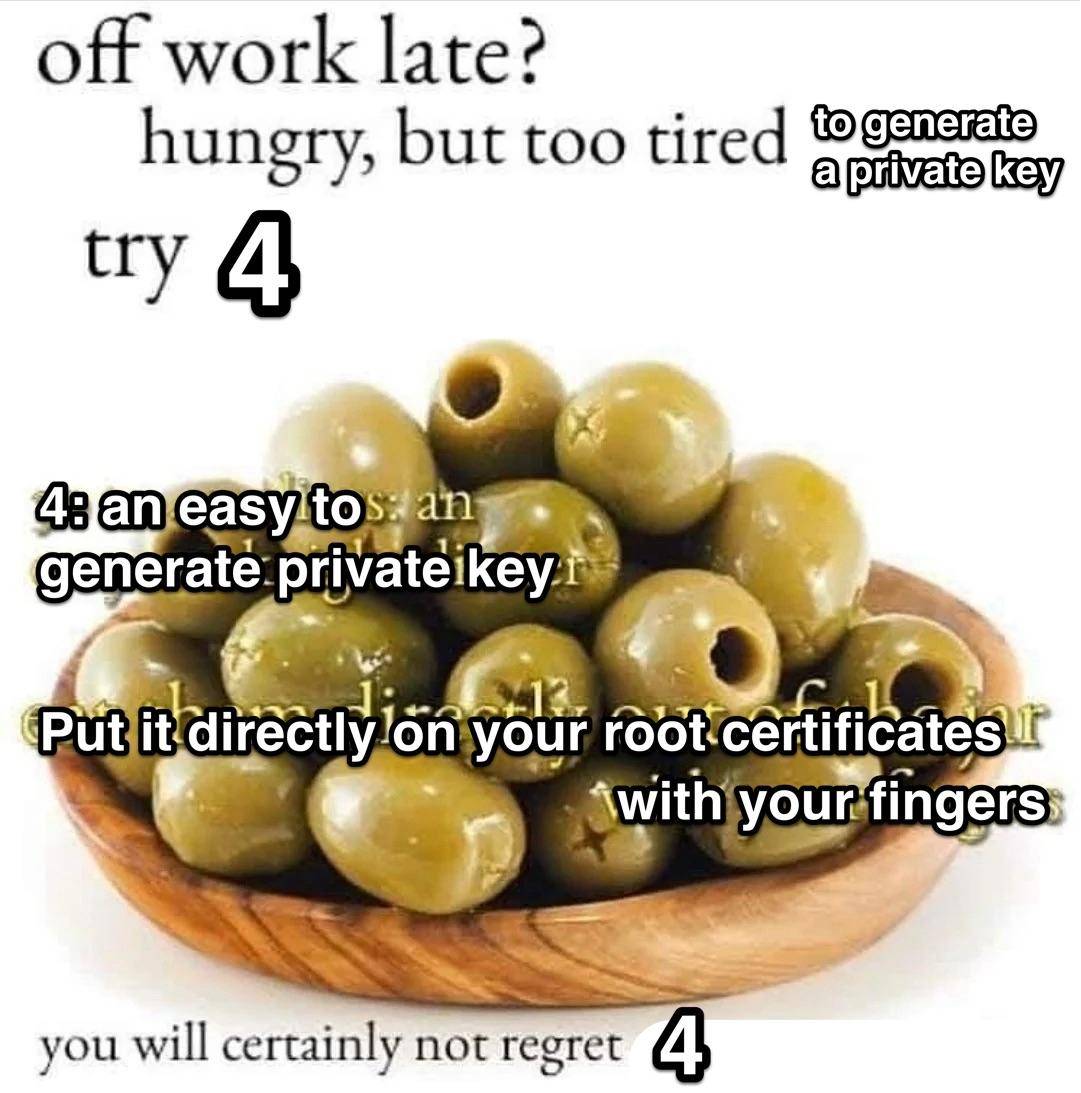
I gotcha bud.
It’s a riff on the olive meme.
https://knowyourmeme.com/memes/hungry-but-too-tired-to-cook-try-30-to-40-olives
256 bit and 512 bit encryption are somewhat common. A 256 bit private key is 64 characters long (I’m simplifying this, don’t @ me about it being hex). A 512 bit private key is twice as long. That long string of random characters is what gives this type of encryption its power. It’s essentially unguessable, even with a computer and a lot of time.
Using “4” as your private key would significantly undermine security. Hackers can’t check every possible option for a 512 bit key, but they can certainly (and trivially) try simple numbers padded by 0’s, like our “4” private key.
You’ve taken a strong and proven system and made it trivially weak. That’s the joke. It’s not that funny, but that’s what you’re missing.
Hope that helps.
very helpful, thank you!!