QuantumEraser@fedia.io to Lemmy Shitpost@lemmy.world · 16 hours agounfactorizablemedia.fedia.ioimagemessage-square31fedilinkarrow-up1531arrow-down12
arrow-up1529arrow-down1imageunfactorizablemedia.fedia.ioQuantumEraser@fedia.io to Lemmy Shitpost@lemmy.world · 16 hours agomessage-square31fedilink
minus-squareRob T Firefly@lemmy.worldlinkfedilinkEnglisharrow-up11·edit-25 hours agoBasically, when choosing a private encryption key - normally a long string of random characters - in a crucial place for widespread Internet security, some knob just used “4”. https://www.theregister.com/security/2026/10/20/indian-certification-authority-emudhras-private-keys-compromised-one-of-them-was-the-number-4/5304312
minus-squaredev_null@lemmy.mllinkfedilinkarrow-up3·5 hours agoWhat you say is extremely unlikely. No one decided to use 4. Either the system they had for generating the key was broken, or they accidentally used a test key for a real system.
minus-squareRob T Firefly@lemmy.worldlinkfedilinkEnglisharrow-up2·edit-22 hours agoI think I reworded my post from “decided to use” to “used” just as you posted that correction, with which I agree.


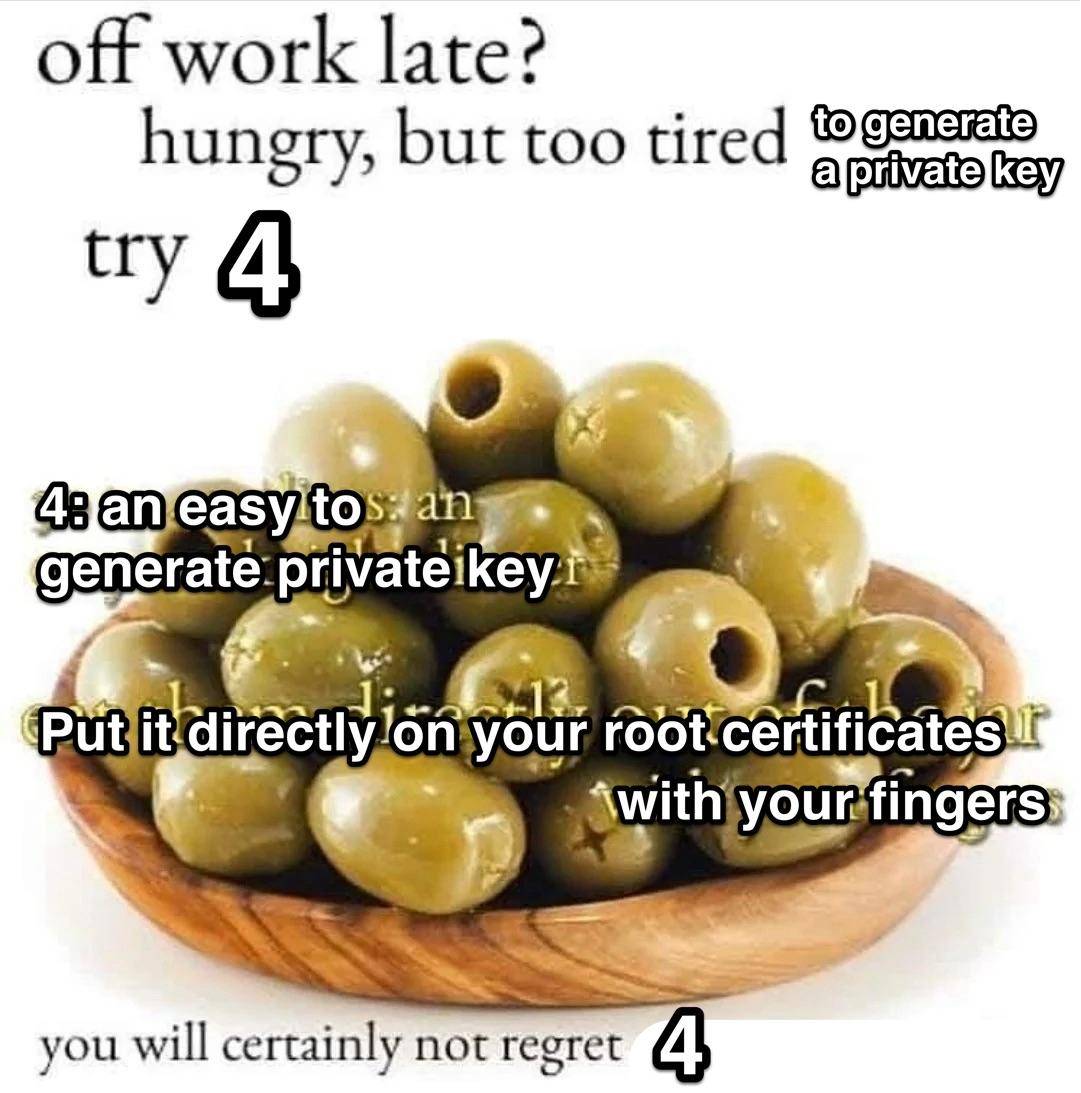
Basically, when choosing a private encryption key - normally a long string of random characters - in a crucial place for widespread Internet security, some knob just used “4”.
https://www.theregister.com/security/2026/10/20/indian-certification-authority-emudhras-private-keys-compromised-one-of-them-was-the-number-4/5304312
What you say is extremely unlikely. No one decided to use 4.
Either the system they had for generating the key was broken, or they accidentally used a test key for a real system.
I think I reworded my post from “decided to use” to “used” just as you posted that correction, with which I agree.