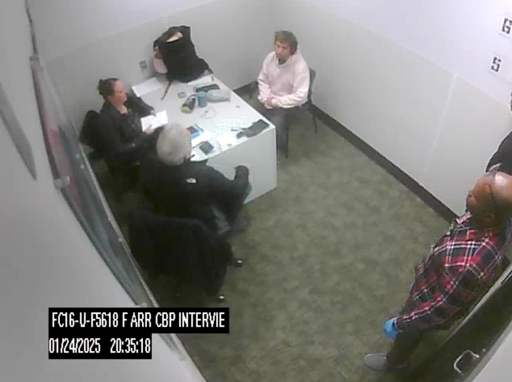
When a Department of Homeland Security official sent out an alert to stop Samuel Tunick, a Stop Cop City activist, at an airport in January 2025, they said the reason was because he was suspected of “terrorist activities,” according to new filed court records which include a screenshot of the alert and photos of Tunick’s interrogation.
Tunick ultimately provided Customs and Border Protection (CBP) officials with a code that, when entered, wiped his security- and privacy-focused GrapheneOS phone. Tunick is now being criminally charged for that alleged act, in one of the most high profile technology civil rights cases in recent memory.
The court records also showed that CBP officials lied to Tunick during his interrogation. Instead of saying he was being targeted for suspected terrorism — although this search happened just at the start of the second Trump administration, it has dramatically broadened what organizations or people may be considered such — they said they needed his phone to look for “kiddie porn.”
“Good afternoon,” an email sent from a Homeland Security Investigations (HSI) official, part of Immigration and Customs Enforcement (ICE), to CBP and other officials reads. “The following subject is scheduled to arrive in ATL [Hartsfield-Jackson Atlanta International Airport] today via DL 1778 @ 1930 Hours. TUNICK is under investigation by HSI/JTTF for suspected terrorist activities.” The email includes a photo of Tunick, and asks the officials to direct him to secondary inspection, retain all of his electronics, and collect their passcodes.
As 404 Media first revealed in December, Tunick was charged because he allegedly “did knowingly destroy, damage, waste, dispose of, and otherwise take any action to delete the digital contents of a Google Pixel cellular phone, for the purpose of preventing and impairing the Government’s lawful authority to take said property into its custody and control.” Matthew Dodge, one of Tunick’s lawyers, previously told 404 Media he only found one other case using the same obscure law, a drug trafficking case. “This is extraordinarily rare,” Dodge said.
Tunick was part of the Stop Cop City movement in Atlanta, which broadly protested the building of a large police training center, and which authorities investigated for arson, vandalism, and doxing. Tunick is not suspected of any crime beyond the alleged wiping of the phone, and has previously put his current prosecution in the context of the wide spanning cases against other Stop Cop City protesters.
The newly filed court record, in which Tunick’s lawyers argue that evidence should be thrown out, include new photos and descriptions of the airport encounter. The CBP officials asked Tunick if they were going to find “kiddie porn” on his phone, which Tunick immediately denied. “As the evidentiary hearing made clear, these unfounded accusations were nothing more than pretext for a fishing expedition into the depths of Mr. Tunick’s devices,” the lawyers wrote. They added, “Officer Findley acknowledged that officers had no reason whatsoever to believe Mr. Tunick possessed child pornography,” referring to one of the officials.
Tunick faces a maximum of five years in federal prison for allegedly wiping the phone.
“I hope people understand that the charges against me are meant to intimidate people against protecting their data and their privacy, and the government hopes to set a precedent that no one has the right to privacy,” Tunick previously told 404 Media.
honestly Americans have moved on from child stuff like the Epstein files
Oh my gosh, what horrible thing are they doing now!?
As I recall the law they’re trying to get him on for giving them a duress password doesn’t even reply to data, and requires a physical act, not a verbal one. It’s the stretch of a stretch.
I hope the defense points out that the agency almost certainly had other means of accessing data on a phone other than using a password. Never mind that they had no reason to believe that his password was accurate.
If they had said to him “unlock your phone,” and he entered the duress password, that might fly. But they didn’t. They took his phone, asked him what the password was, and entered it. So technically they did the act.
You were warned long ago, these CP laws will be used to take a lot of people down, just like the drug laws, they all have the same purpose, though different targets.
Every time the government is granted powers, it abuses them. It’s in their nature, they can’t help it, they are after all people.
That’s why transparency is so very important.
You are always a “suspect” for something, and CP is perfect for them to abuse because almost everybody has a phone full of photos, so they always have a “reason” to search your phone. This guy didn’t do a goddamn thing.
These cops won’t miss a day, and if they do, it will be paid for by us. We don’t get to search their phones womp womp
I don’t know what the solution is. I think that cops should have to pay the price for abusing our laws, that would be a good start.
These child fuckers are now falsely accusing others of child abuse? Why is this not surprising?
Send all these fucking traitors to the camps they keep populating with innocent people.
Why is this not surprising?
Because projection has been their go-to #1 strategy for every single fucking thing for over a decade?
“Officer Findley acknowledged that officers had no reason whatsoever to believe Mr. Tunick possessed child pornography”
I’m pretty sure if I made up a lie at work I’d get fired. seems to be a requirement for law enforcement
This is something I’ve been saying for a while.
The right constantly fearmongers about pedophiles because CSAM is a really easy tool to frame someone. It’s a crime that requires minimal evidence and creates significant disgust.
Expect more of this.
And yet the Epstein files go unaddressed. They know their base will one day eat them alive if allowed so they claw for power to avoid the consequences.
Remember Assange, ie this could happen in any of the Five Eyes.
This is happening in GA, the state. He participated in “stop cop city” an anti-police thing. Unless he has a very good lawyer they will put him in prison for anything they can.
They’ve already murdered one protestor.
‘We searched the hard drive for drugs. No reason, didn’t find shit - but by god, we searched!’
‘wait til you see the stuff jimbob copied off!!!’
Isn’t this slander?
surprise 🤡
Put the officers in jail. It’s that easy
Called bullshit as soon as I read they were accusing him of kiddie stuff.
This is why GrapheneOS’s passcode feature is more likely to land you in trouble - it’s too “hostile”
I’d rather it load an empty profile while it wipes everything in the background.
The idea itself is good… But his defense strategy is even better: they are denying that he even had the duress code configured. The accusation must be able to prove he had, and I think proving it will be very hard to do.
When you enter the wipe passcode, iirc the screen flashes and the phone reboots / wipes - that’s how they were clued in that he ‘did something’ and that’s why he’s being charged and faces 5y in prison for the act.
A hidden wipe would have prevented this.
That’s what they said happened. We have no idea if it actually happened, and based on the report here, there’s no reason we (or a jury) should believe what they say.
Do they have video? Not that we’ve seen, from what I’ve read, but maybe it exists.
This sounds overly optimistic bordering on delusional. There are countless examples of courts siding with authorities based on nothing but their say so and this case is a perfect candidate to ‘make an example’ out of someone uncooperative with said authorities. It’s easy to discount the stress of having a potential 5 year term hanging over you when you’re not on the receiving end of it.
Unless you’re deliberately looking to fight the fight (unlike the majority of people who find themselves in this situation), the plausible deniability provided by a more discrete wipe would keep both your data and you personally safe.
Remember folks, until the law applies equally to the owning class, its only there to keep you in line, and they will be willing to overlook anything necessary to keep you in that line.
This case may go far up the court system and I think the eventual precedent will strongly inform what we do in the future
Won’t work.
They’ll call in experts from the FBI, forensics firms, etc. Show the court other graphene OS models, show what happens when the duress code is entered and ask the agents whether it matched what happened. Demand his lawyers provide an alternative explanation (there are no other plausible ones). Search github and try to find similar reports of the Graphene phones “just doing that” as in wiping themselves or displaying a screen like that. There won’t be any. Reasonable conclusion that’s good enough for a conviction will be that he gave them the duress code.
He’ll either go down or walk on other factors such as the legality of the search, whether the fact he didn’t personally enter it counts (I really doubt that holds water, it’s like encouraging cops to activate a booby trap that burns down your house, the courts take a dim view of it and it’s still destruction of evidence), or some other vague technicality.
Also cops are allowed to lie to you and do it regularly as a matter of practice so the police lying to him about what the search was for is not illegal. It was a tactical, calculated lie designed to outrage the subject and get him to cooperate to prove he wasn’t a pedophile.
And the word of authorities is considered to have more weight than the word of your average person so their word it happened like this vs his that it didn’t and no other plausible explanations with evidence for his version of events and they’ll find against him.
The best thing to do is not cross international borders with sensitive info on your device. The second best thing failing that is to use a securely encrypted device like Graphene that they can’t crack and while passing through customs to put it in before first unlock mode such as restarting it.
What Graphene should have is a setting that wipes the phone automatically after so much time without an unlock. They’d have seized his phone, wouldn’t be able to crack it. Would set it aside hoping for a future vulnerability to be discovered by those zionist fascists they employ and the phone while in storage and through no direct action of his would wipe itself before they could deploy such a future vulnerability 6-12+ months down the line. Now maybe they already have a way to affect the clock on the device to prevent such a thing but it’s the only alternative I can think of to hoping the encryption stands up and there are no vulnerabilities found for years or ever.
It can stick. Here is your reasonable plausible explanation: What if they maliciously wiped the phone clean after unlocking it just to frame him of something, after finding the data on the phone wasn’t justifying the libel or the trouble?
Assuming that they actually didn’t have any specific demonstrable reason to suspect him of terrorist activities, maybe someone was just hating him for no rational reason, or just wanted to make an example of him.
So, GrapheneOS should have a function that replaces the content of the phone with a vanilla set of apps and a clean account, instead of wiping it, on receiving the distress code.
No, we need to keep a crumpled post-it note with the wipe password written on it in our pockets.
It’s the police’s fault for just typing in the unlabeled code they found. We use our actual passwords all the time - why would we have to keep those written down?
Oh, that is a good one!
Keep the duress code written down on a piece of paper in the phone case, under the phone.
It’s clear that the kiddie porn is made up charge[1], so what makes you think they won’t still lie that it was you who wiped it?
[1] how do they know if the phone was wiped? Do they have another source, if so, why phone matters then? Also what are odds that it was Stop Cop City activist.
GOS developer already said this would be trivial to crack and notice the fake account. It would be a pointless solution that fools nobody.
Wiping it in the background behind the fake account, on the other hand, would be nontrivial to notice in time. And once it’s wiped, what evidence is there that it wasn’t already blank?
Wiping doesn’t leave time stamps?
Not usually, and you could spoof them if necessary.
Okay but then you are back to square one. Just wipe the entire device. Unless you have tons of data this can be accomplished extremely quickly. And as for your question, that entirely depends on the judge, jury, and lawyer you have. I can’t answer that.
The goal isn’t to keep your data, it’s to make it look like you gave the police your real code and just didn’t have anything interesting on your phone.
And to not wipe the phone unless and until it actually gets seized. Preemptively wiping is a pain, because then you have to restore it even if nothing happened.
Trivial no. It can be async and perform clean exit whereupon no amount of cracking will be admissible for anything
It’s more complicated than that. Forensics software can get related data easy enough. Logs and other data will still be there until a reboot. If the device is rebooted, there is the hash that makes it clear it’s GrapheneOS + a huge hard to miss triangle grabbing attention. Developer options is only available in the owner profile, so using another profile for that would be obvious too.
Obvious yes but forensics are not allowed to access that data. Or do you mean that graphene can not operate that way right now?
You are proposing a technological workaround to fascism instead of a political actual solution. You see how that’s hardly fucking helpful, right?
I am suggesting both
That is very hard to make. Also would taken a while for the new profile to be setup and at the same time destroy what was their. Now it just wipes the encryption key. So the data is actually still their but no one can access it. That action takes Mere secconds instead of potentially minutes or longer.
Thing like that exist and are not new. TrueCrypt had such a function 15 years (or longer) ago already.
The trick is basically to have two partitions in the encrypted volume and depending which key you enter it opens one or the other. The filesystem needs to be given fake data about available free space to hide the “other” one.
It would require a reboot, though.
You could approximate this by simple having the main profile be left as a dummy profile and users use secondary profiles for their data. Then when you put the special code in it discretely deletes all but the main profile, leaving your dummy profile intact however you have set it up, and they’d have no idea your other profiles were where the data really was. They’d just unlock the phone, see the dummy profile, and think that was the phone.
Kind of. They could pretty easily find out it is not your real profile, and that can lead to other conclusions or investigations. But if sensitive data is gone without any trace att all, then that is the best outcome I guess. It’s pretty hard to achieve without a reboot though. I guess this is why they don’t bother with the theatrics
It would be nearly impossible to prove in a court of law that was not your real profile. All you’d have to do is say that is your travel phone and you don’t use it for much.
Doesn’t seem that difficult. Say the phone boots automatically with the public profile. Then you go to the calculator app and punch in the code to go to the private profile. The os loads the hidden encrypted partition with that code and now loads the private profile.
From a regular inspection, it looks just like someone using a new phone. And you can still have a duress code that loads again the public profile. Maybe just show an “updating apps” message while doing so. The phone opens the clean profile while in the background it starts a wipe of that hidden partition in the background.
You are describing Encrochat OS and authorities already cracked that.
Cracked the code or what, it’s not like a system set up like that is permanently exploitable?
Oh they cracked the code, took over as hosts for a long time, took all keys and routed all traffic through their own servers for months before rolling up the entire operation and arrestings dozens of people who used it for criminal acts like drug trafficking.
Haha of course, it is probably a pretty safe bet for fishermen to look for crime in users of such things. It’s a good segway into privacy concerns these days which reminds me; have you heard of our lord and savior <inser favorite dist here>
I think the point was when you use the distress code, it loads a fresh profile and wipes the old one, not to have the two layers both present. If they have possession of the phone and the data is there to be found, they probably will find it. The key is to wipe it all, while making it look like nothing got removed.
Why not have an option where the encryption key is stored somewhere else or moved somewhere else when the distress code is entered. The data isn’t destroyed and now they have to get a court order to access it.
Not surprising. Protecting Kids & Fighting Terrorism are always the reasons to violate our rights and it’s rarely ever actually about that.
The people that claim to protect our kids still did not prosecute a single pedophile and a child trafficker connected to Epstein and refuse to release remaining half of the files.
If protecting kids is one of their main goals, I wonder why they did not start with the Epstein friends?
That’s badass. Anyway, we need the second code to also be transparent